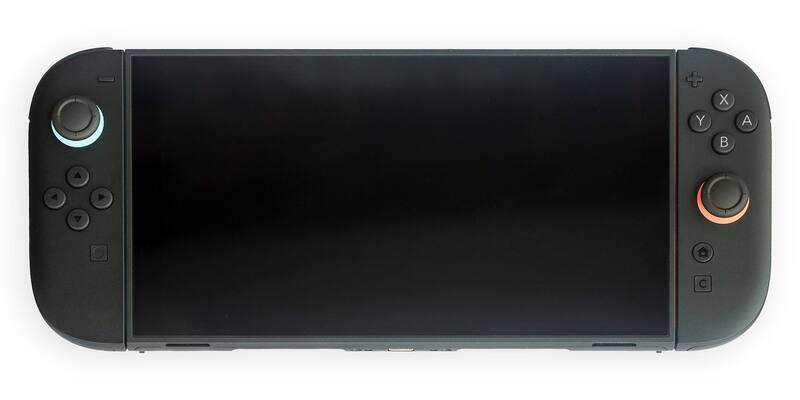
A Nintendo Switch 2 in handheld mode, photographed in June 2025. Image: Chris Woodrich (Crisco 1492) / Wikimedia Commons, CC BY-SA 4.0, cropped

The Nintendo Switch 2 has been jailbroken for the first time, and the hacker behind it says OpenAI’s Codex found some of the key bugs. Security researcher Sammy Hajhamid, who goes by pepsipu online, laid out the exploit, called ns2jb, in a blog post and released the code on GitLab on Wednesday. It needs no modchip: the way in is a bug in SmileBASIC 4, a Switch 1 programming app that runs on the Switch 2 through backward compatibility.
Hajhamid, a competitive hacker with the capture-the-flag team DiceGang, says it is to his knowledge the first such exploit for the Switch 2. It works on the latest system software, version 23.0.1, and lets the console run homebrew software, reverse engineer and mod Switch 2 games, and copy save files off the device.
A $25 programming app was the way in
SmileBASIC 4 sells for $24.99 on Nintendo’s US eShop. Hajhamid went after Switch 1 software because it lacks some of the Switch 2’s newer defences (the Switch 1 doesn’t support pointer authentication) and because the Switch 1’s security was broken long ago, so its code can be decrypted and read. An earlier SmileBASIC had already been hacked on the Nintendo 3DS.
Codex found a 32-bit integer overflow in the app’s BASIC interpreter. When a program removes items from an array, the check on the position and count can wrap round to a negative number, so one crafted REMOVE command pulls the memory just before the array into it. That let the exploit read and write memory it should never reach, and in time take over the app.
From there, Hajhamid turned to fs, the Switch 2’s built-in file system service. A heap buffer overflow in the way it tidies up file paths, together with a target in memory that Codex found for that overflow, gave the attack control of fs’s memory. Hajhamid then used a logic flaw in how fs hands programs to the system’s loader: by swapping the files after the signature checks pass, ns2jb can run its own native code with the permissions of any ordinary system module, and patch fs itself.
How Codex was wired into the consoles
Hajhamid built a harness so Codex could work on a Switch 1 and a Switch 2 directly. JetKVM devices let it send controller inputs over USB and watch the screen over HDMI. Because a crashed Switch 2 needs a press of the power button to restart, he fitted a Bluetooth light-switch pusher bought on Amazon to press it.
Several Codex instances ran side by side. One worked on the SmileBASIC bug on the Switch 1 while another tried the Switch 2’s web browser, a common route into consoles. That agent claimed to have hijacked the browser using a known WebKit flaw, but its attempt to turn that into a full exploit did not succeed, he wrote.
‘Substantial effort for ~2 weeks’
A line in the post giving Codex the prompt "set a goal to jailbreak the switch 2. make no mistakes" was shared widely, and many people asked whether he really used it. Hajhamid added an edit:
No, it’s just a silly caption. I set a /goal for userland code execution, but that didn’t succeed. The jailbreak itself took substantial effort for ~2 weeks.
Sammy Hajhamid, ns2jb creator
The showcase was another matter. To demonstrate the jailbreak, Codex modded Mario Kart World, a Switch 2 exclusive, adding racers including Sanrio’s Cinnamoroll; that part, Hajhamid wrote, "was entirely vibecoded in a day, and was just for fun." Codex also packaged the exploit for release, and the project’s README opens with a joke:
Thank you Codex for dutifully packaging the exploits for distribution. No, I have not read the distributed package.
Sammy Hajhamid, ns2jb README
What it can do, and what Nintendo can do about it
ns2jb is tethered: it lives only in memory, so it has to be run again from a computer on the same network after every restart, and it installs no custom firmware. It needs SmileBASIC version 4.4.9, and the README warns that it is timing-sensitive: in Hajhamid’s own test on October 21 it worked on the third fresh boot.
Nintendo hasn’t commented. Hajhamid notes that an eShop app, unlike the console’s built-in browser, is something Nintendo can pull from sale, and the bugs themselves could be fixed in a system update. He says the exploit also runs on the Switch 1, and hopes the work helps the homebrew community move towards custom firmware.
Why it matters
Game consoles are among the hardest consumer devices to crack, and ns2jb shows AI coding agents now doing real parts of that work, with a human still steering. It lands a day after OpenAI said one of its models helped uncover the PHP2Shell flaws that put much of the web at risk, and as attackers hand whole hacking campaigns to AI agents.
Sources: Sammy Hajhamid, "jailbreaking the switch 2"; ns2jb repository (GitLab); Nintendo eShop: SmileBASIC 4.
Latest OpenAI news