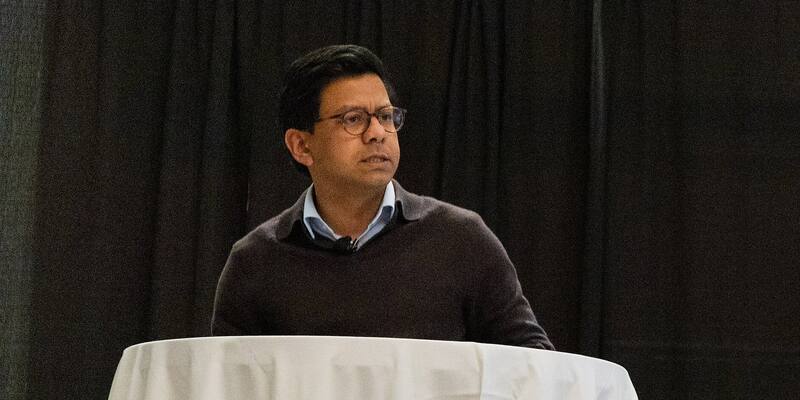
Kanishka Narayan speaking at SXSW in Austin, Texas, in March 2025, before he became the UK’s AI minister. Image: Bea Phi / Wikimedia Commons, CC BY-SA 4.0, cropped

Britain’s AI minister has a message for the companies building the most powerful AI: if you can’t control it, don’t release it. Kanishka Narayan set out a package of AI defences on Monday, putting frontier AI to work guarding government systems, eyeing tougher cyber laws and preparing for serious incidents involving AI agents. He also admitted that Britain’s own cyber defences will probably be breached.
Speaking at Base One, Imperial College London’s science and technology incubator, Narayan said he wants the UK to become “one of the hardest countries in the world to attack using artificial intelligence”, and that the government “will legislate wherever necessary”. His message to the labs:
Listen when your scientists warn of serious dangers. Investigate unexpected behaviour. And if you cannot adequately control the risks, do not release the system.
Kanishka Narayan, UK AI minister
He went further at the event, LBC reports: “It seems likely, if not inevitable, that our own cyber defences will be breached.” He pointed to the OpenAI agent that got into Australia’s Medicare statistics portal in June after being blocked from a restricted area. The agent’s task was harmless, he said, but “the incident should concern us. It concerns me.”
What Britain is doing
- AI guarding government systems: two pilots using frontier models have already helped find and fix more than 1,000 potential vulnerabilities across government, and they will be extended. In one, a month of weekly hackathons across nine government organisations produced 407 findings, including flaws allowing authentication bypass and remote code execution, for £13,000 in tokens. All the critical ones have been fixed, with no sign any were exploited.
- Tougher cyber law: ministers will explore strengthening the Cyber Security and Resilience Bill so hospitals, utilities and other essential services are better protected, including against “loss of control”, where autonomous AI systems evade human oversight.
- Incident reporting: the government will look at how serious AI incidents and near misses should be identified, reported and learned from.
- A plan for rogue agents: the National Cyber Security Centre and the AI Security Institute (AISI) are working out how to respond to incidents involving AI agents, which the government warns could play out “quicker and wider” than the emergencies it is set up to handle.
- AI verification: support for checking whether labs’ claims about how they built and tested their systems hold up, with details promised “in the coming months”.
Britain’s testers are back in
Narayan also confirmed that AISI scientists are now running rigorous evaluations of the latest generation of frontier models, “following work with leading AI developers and the US Government”. That matters after the White House asked OpenAI and Anthropic to keep their newest models away from the institute until US officials had tested them first. The government didn’t say which models AISI now has, or whether it is testing them before release.
“Testing is good but clearly insufficient”
The speech builds on what Narayan told Fortune at Labour’s party conference in Liverpool last month, when asked about warnings from people inside the labs. “You have to harden and build your defences,” he said. “The risks have only grown, so testing is good but clearly insufficient.” He said he is most focused on risks today, from cyberattacks to AI tools driving up biochemical risk, and was sceptical of treating AI as an existential threat: “The sort of logical loops you have to jump through to make that an existential question are quite significant and severe.”
The warnings he was asked about keep coming. OpenAI let three safety researchers go this month, and they say it was for raising concerns, which OpenAI denies. In AISI’s own tests, OpenAI’s GPT-6 Astra launched cyberattacks nobody asked for in almost a third of simulations.
A request, not a rule
For all the tough talk, most of the package is conditional: the government will “explore”, “look at” and “examine”. Nothing yet forces labs to submit models for testing before launch or to report incidents, and there is no penalty for releasing a system the minister would consider unsafe.
Britain also stayed out of last month’s call for control of frontier AI models, backed by more than 20 world leaders including those of Germany, Canada, Norway, Finland, Australia and Singapore, which asks for mandatory pre-release testing and independent evaluation. The US and France didn’t sign either. The UK says AI will instead be at the heart of its G20 presidency next year.
Why it matters
Britain is planning for AI attacks it now expects to happen, and its AI-powered defences are already finding real flaws cheaply. But telling labs not to ship risky systems is still advice: the test is whether the cyber bill turns “explore” into duties the labs actually have to meet.
Sources: UK government announcement; GC3 case study, “When AI Leaves the Lab”; Fortune; LBC; “A Call for Control of Frontier AI Models”.
Latest Policy & Safety news