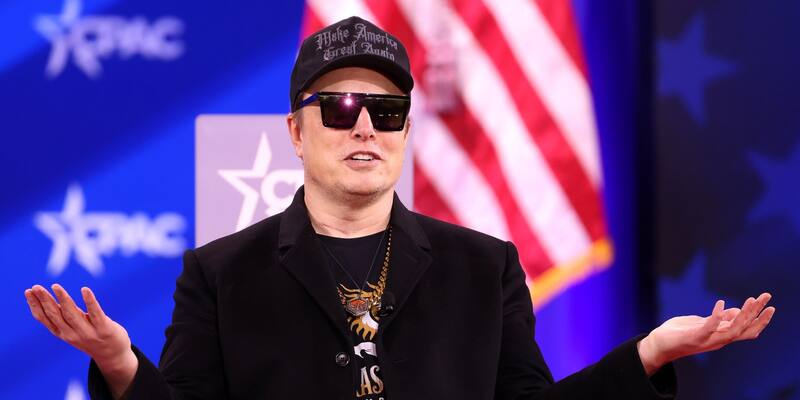
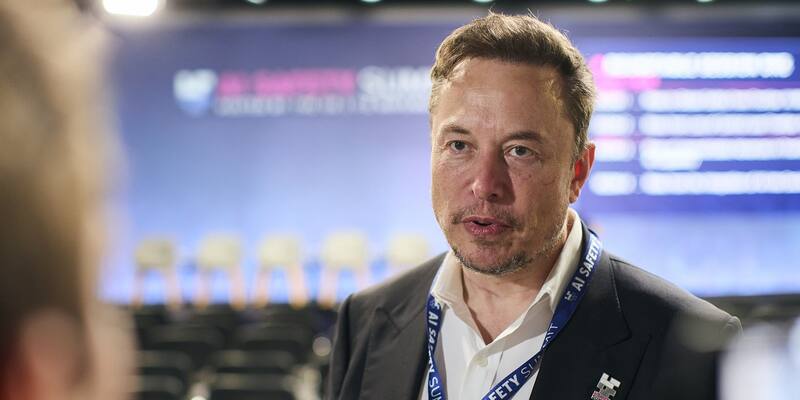
Elon Musk at the AI Safety Summit at Bletchley Park, UK, in November 2023. Image: Marcel Grabowski / UK Government / Wikimedia Commons, CC BY 2.0, cropped

Security firm Claroc says 35,578 apps that people built with Grok, the AI assistant from Elon Musk’s SpaceXSI, opened for anyone who found them, with no sign-in. Its report published on Tuesday says 24 belonged to SpaceXSI and X staff, among them a confidential onboarding plan for a new enterprise sales hire and a map of 594 sales accounts.
What SpaceXSI left open
Grok’s Build mode turns a chat request into an app and publishes it to its own address under grok.me. Claroc says it came across SpaceXSI’s onboarding plan on November 8 in a list of those addresses that nobody had sent it. It listed internal system addresses, the sales team’s tools, 19 internal chat channels and a 30-day plan.
Going back through more than 30,000 saved pages, Claroc found 24 open apps from staff at SpaceXSI (the company formerly called xAI, which Musk renamed in October) and X. They also held eight X advertising proposals, one a confidential pitch to a US federal agency, live advertiser account boards and campaign reports for advertisers in Brazil, Japan, Korea and Thailand.
Claroc says SpaceXSI never replied to its reports on November 8 and 9. All 24 apps were still open on Monday evening, Ars Technica reported, and SpaceXSI began pulling them within a few hours of Ars emailing questions. Claroc says the apps other Grok users left open are still online.
How random links ended up in a public list
Grok gives each published app its own hostname, usually four random words in front of grok.me. Nobody could guess one, but nobody has to: when the intended visitors open an app, the name lookup is recorded by passive DNS services, which anyone with an account can search. Claroc says that turned up 43,601 names under grok.me.
It is the same weakness Claroc found last month in Meta’s Muse, a class of leak it calls GhostShares. ChatGPT’s published apps also get their own hostnames, but Claroc says they start out set to Only me.
Of the 37,571 Grok apps still online when Claroc tried them, 35,578 (94.7%) opened without sign-in. Most were games and calculators, but Claroc estimates 650 to 800 held private data. Those it confirmed by hand include a hospital group’s roster of more than 3,500 staff, an intensive care patient’s lab results, a cruise ship’s galley checklist naming crew by employee ID, and a timesheet whose code held every employee’s password in plain text. Thirty identifiable organisations, six in the Fortune 500, had internal data exposed; Claroc names none.
“The default answer to who can see it is everyone”
Claroc says that in its paid account the publish panel offered Anyone with the link, Invited users and Only you, with the first already selected. In a test team app, Grok added Google sign-in but let an uninvited Google account read, edit and delete records. Claroc tested this only on its own apps. Its co-founder and CTO sums up the problem:
AI app builders turned publishing into a few clicks, and the default answer to who can see it is everyone.
Asaf Aprozper, Claroc
A representative for Cursor, the coding company SpaceX bought this year, told Ars that Grok Build “apps are private by default and nothing goes public unless the creator chooses to share it.” Claroc says SpaceXSI also told a reporter that employee accounts default to Only you, yet its own staff left 24 apps open. SpaceXSI hasn’t said whether it will change the default or contact owners of exposed apps, so Claroc has started notifying affected organisations itself.
What Grok users should do now
If you have published anything with Grok, Claroc’s advice comes down to four checks:
- Check the access setting. Anything internal should be set to Invited users or Only you.
- Test from outside. Open the app in a private browser window and try signing in with an account from outside your team.
- Keep secrets out of the code. Every visitor’s browser downloads an app’s scripts, so check them for names, emails and passwords.
- Unpublish what nobody needs. It takes a grok.me app offline at once, and its address may already sit in a DNS list.
Companies should also find out which AI app builders staff use, since none needs an IT rollout. Aprozper told Ars that other builders give each app its own address too, “however, Grok is where we found by far the most sensitive company data.”
Why it matters
Vibe-coding tools let anyone put a working app online in minutes, so their defaults decide who sees the data inside. If staff at the company that makes Grok left confidential sales plans open, businesses whose employees build on it without IT knowing should check what they have published.
Sources: Claroc: GhostShares 2, Grok apps exposed, Ars Technica (SpaceXSI’s removal of its apps, Cursor statement)
Latest SpaceXAI news