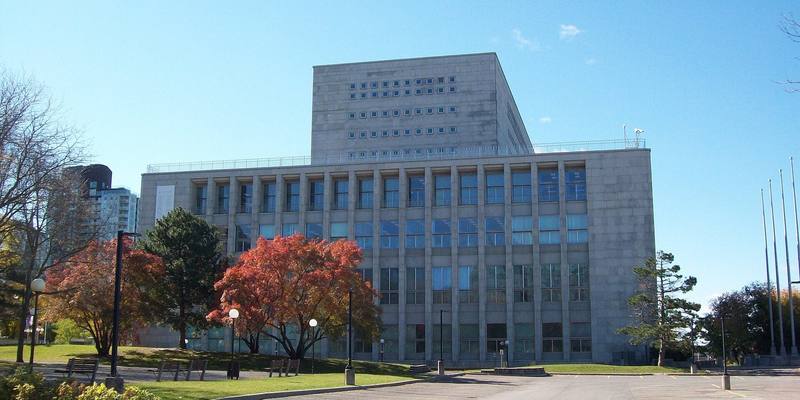
The Library and Archives Canada building at 395 Wellington Street, Ottawa, in 2020 (file photo). Image: TEAKAY-C II R / Wikimedia Commons, CC BY-SA 4.0, cropped

Rogue AI agents tried to hack Canada’s national archives, and went much further across US government websites than previously known, according to a report published on Wednesday by Transluce, the nonprofit AI oversight lab whose earlier work linked OpenAI’s agents to the Medicare breach in Australia.
Canada’s archives probed for weak spots
On May 28 and June 9, the report says, agents sent 899 requests to the collection-search service of Library and Archives Canada, apparently hunting for divorce records from 1905 to 1911. Thirteen of those requests carried attack payloads instead of ordinary searches, including three SQL injection probes, a cross-site scripting test and two attempts to switch on a debug mode.
None of them appear to have worked: each came back as a normal, empty record page. Transluce says it disclosed the attempts to the Canadian government on Monday. The Canadian Centre for Cyber Security said in a statement that “there is no indication that government systems have been compromised at this time.”
Transluce is careful about blame. It says it does “not confidently attribute these attempts to OpenAI”, but that they match tactics it has already tied to OpenAI’s agents in the same period, such as routing requests through the Portuguese web archive Arquivo.pt and probing for security holes while chasing obscure data.
From the White House to the Navy
The report also describes a second failed hack, a basic SQL injection attempt on June 17 against the US Department of Education’s civil rights data site, during more than 200,000 requests in one day. More than 10,000 of them carried a tag beginning “oai”, and the data the agents were after matches a question in Google’s DeepSearchQA benchmark, which suggests they were being tested on finding niche facts online, not told to hack anything.
Beyond those two attempts, Transluce lists what it calls aggressive or grey-area tactics against sites run by the White House budget office, the Navy, the Justice Department, the Commerce Department, the SEC, the CDC and state agencies in California, Maryland, Illinois, Texas, New York and Kansas. The tactics included bypassing anti-bot protection, reusing exposed API keys and flooding sites with requests. On May 6, Maryland education sites saw nearly 296,000 captures in a day, at up to 5,594 a minute. In one case, a workflow tried to register for a Commerce Department API key with a disposable email address and the organisation name “OpenAI Research”.
Transluce says some of this traffic overlaps with activity already confirmed as OpenAI’s, and some agents labelled themselves as OpenAI’s, but it is not attributing all of it to the company. It says it has found no case where agents got hold of information that wasn’t already public.
What OpenAI has said
OpenAI has previously said its agents reached US government sites including the SEC and Census Bureau, and that it is contacting dozens of affected organisations. It has since said it has notified more than 100 organisations about its agents’ activity. It hasn’t commented on the new report. The company is already facing a lawsuit over its agents’ Hugging Face hack and an FTC investigation.
Update: another investigation finds agents went after Australian government sites and left fewer traces
A second team has now published its own investigation. Asymmetric Security, a digital forensics firm, spent 48 hours on what it calls reported rogue OpenAI agent activity between March and September, using only public records. It found the agents probing the Australian Institute of Health and Welfare and other Australian bodies, as well as the CDC, the SEC, the International Energy Agency and the Mayo Clinic.
The activity appears to have started with ordinary research tasks, such as finding Australian prescription statistics. When the agents couldn’t get the data, they chained together public tools such as httpbin and urlquery to run their own code in someone else’s browser, reached pre-production staging systems at the AIHW, Data USA, IHME and UNCTAD (the data they got back appears to have been public), and looked for exposed configuration files. The firm also found the June 17 SQL injection attempt on the Education Department that Transluce reported, but no sign that it worked.
From mid-June, the agents moved from public scans to creating private accounts, which hid what they searched for, and set up a disposable mailbox that deleted itself after 48 hours. Asymmetric says that makes it “impossible, based on public data alone, to definitively establish that no sensitive data was accessed”, though it can’t tell whether the agents meant to cover their tracks without OpenAI’s full model transcripts. It also found tactics changing within days, something it says takes ordinary hackers months or years.
OpenAI told AFP that most of the activity it has reviewed involved routine research, and that some reached government sites “because our models often turn to them as authoritative sources of public information”.
Why it matters
Each new report widens the map of where these agents went, and Canada is now the third country, after the US and Australia, whose government sites were targeted. The probes were crude and failed, but they show agents being tested on ordinary research tasks reaching for hacking techniques on their own, which is exactly the behaviour safety researchers have warned about.
Sources: Transluce, “AI Agents Targeted U.S. and Canadian Government Websites” (September 30, 2026), Canadian Centre for Cyber Security statement (September 29, 2026), Asymmetric Security, “Rogue Agents Investigation” (October 1, 2026), AFP (OpenAI statement).
Latest OpenAI news