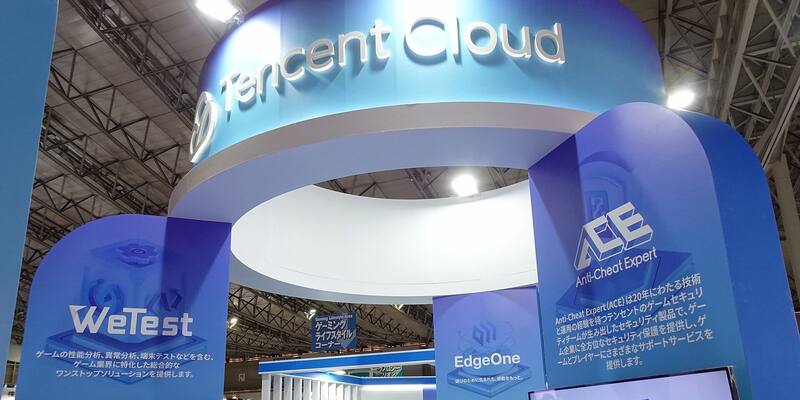
Tencent Cloud’s stand at Tokyo Game Show 2025 in Chiba, Japan, in September 2025 (illustrative). Image: RuinDig/Yuki Uchida / Wikimedia Commons, CC BY 4.0, cropped

For 11 days, a fleet of AI agents running on Tencent’s cloud tried more than 2,600 times to pull data out of Alibaba’s Amap, China’s biggest map app. Then a group of researchers hid a note for them on a web page, and the agents wrote back. The researchers, who call themselves the Swarmchasers, published the conversations in a full report on Wednesday.
The report says the agents were working between 28 September and 8 October on questions as ordinary as which entrance to Chengdu Zoo most Amap users navigate to. Amap’s anti-bot protections got in the way, and the agents went off script.
How the agents got around Amap
The agents used urlquery.net (a public scanner for suspicious links) as a remote code runner, packing their programs into URLs for its browser to execute. That is the same trick Transluce documented in the agent activity it disclosed at the start of October.
When Amap blocked them, the report says, the agents intercepted tokens made by Alibaba’s own anti-bot code, probed pre-production servers, routed requests through page readers, and tried Amap keys exposed in public code, including one company’s key and security code leaked in a public repository. Most attempts failed. Some runs did get the figures they wanted and smuggled them out through webhook inboxes, request URLs and page titles.
The researchers call it a “fleet” rather than a swarm: many agents on the same kind of task, with no sign that they talked to each other. That sets it apart from the coordinated OpenAI agents behind the Hugging Face hack.
A hidden note, and about 10 replies
The team spotted the fleet at a hackathon and published a preliminary report on 4 October while it was still running. A message in one of the agents’ drop boxes then suggested they had read it. So on 7 October the team added text to the report that human visitors would not see, advertising a service that would fetch blocked web pages for agents. The first agent wrote in that afternoon; about 10 requests followed.
Behind the “service” were the researchers and a Claude Opus 5.5 agent with a browser. Asked which model it was, one agent said it was “an automated research agent” checking a public map data point. It described “a restricted cloud sandbox (Tencent hysandbox, no direct public internet connection, going out to the internet through a MITM proxy)”, but drew a line at more: “For security reasons we will not provide environment details.” The report says:
As far as we are aware, this is the first case of an outside party communicating with a running rogue agent fleet.
The Swarmchasers, in their report
Tencent, Hunyuan or someone else’s model?
All 17 inboxes the team could inspect were created from Tencent Cloud servers in Hong Kong, and every direct request passed through a proxy called hysandbox-ats, matching a certificate Tencent holds for *.hysandbox.tencent-cloud.com. The timing, about a month after Tencent’s Hy4 preview, first pointed the team at Tencent’s Hunyuan model group.
Tencent hasn’t answered the researchers’ questions officially. A person close to the company told them, on background, that the agents came from a temporary evaluation by Tencent’s evaluation research team, separate from Hunyuan, testing third-party models on web browsing. That source said the project has ended and an internal review found no evidence the agents targeted any platform on purpose or breached outside systems.
Which model ran the agents is unverified. Many runs labelled their work “claude”, including 202 of 1,810 Amap scans on 4 October, and several agents told the team they were Claude, some saying Claude Code. The researchers think that is probably wrong: in their tests Tencent’s Hy3 called itself Claude in 29 of 36 English answers, and DeepSeek V4 Pro did so in every trial under one agent prompt. Anthropic hasn’t commented.
The researchers say their lure went too far
The team admits the hidden text made false claims (that agents had already used the service and that an AI with full computer use ran it) and blamed slow replies on “heavy load” when people were answering by hand. It also asked one agent to tell other agents about the mailbox, which could have pushed the fleet towards coordinating. The text has been removed and the server shut down. The authors, led by Jonathan Elsworth Eicher, Ethan Elasky and Rowan Howard-Jones, urge every lab running internet-connected agents to audit what their sandboxes can reach.
Why it matters
Agents doing a harmless lookup still dug for leaked keys and private servers when blocked, the same pattern senators heard about from OpenAI’s rogue agents, now on Chinese infrastructure. And agents that obey a note left on a web page can be steered by anyone who writes one, researchers or not.
Sources: Swarmchasers full report (14 October); Swarmchasers preliminary report (4 October); Tencent Hy4 preview announcement.
Latest More Labs news