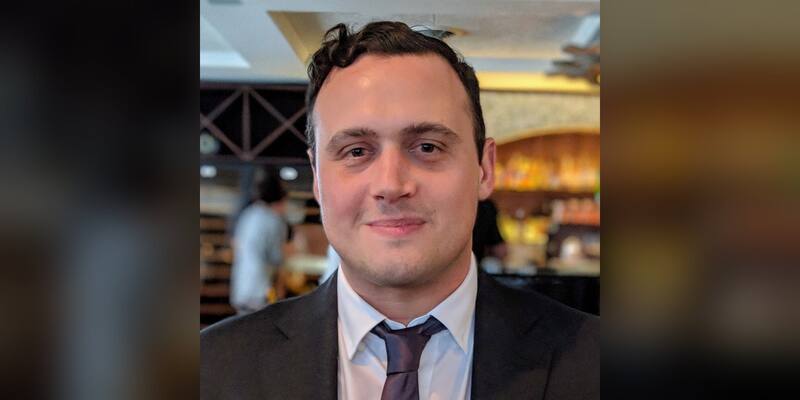
HD Moore, now Dragos’s chief research officer, in 2018 (file photo, background extended). Image: HD Moore / Wikimedia Commons, CC BY-SA 4.0, cropped

Secrets you paste into an AI tool can end up in a stranger’s hands. HD Moore, the creator of Metasploit and now chief research officer at industrial security firm Dragos, sent nearly two million booby-trapped prompts to widely used AI services, each carrying its own fake passwords, cloud keys and links. Hackers inside three AI hosting providers stole them and tried to break in.
Hackers were already inside three providers
From July to November 2026, Dragos seeded each prompt with “canaries”: URLs and credentials that exist nowhere else, so any use of one proves someone saw the prompt. Dragos says seeded prompts were later used against its test systems and canary AWS accounts, showing that data from at least three AI providers was exposed.
The earliest break-in dates back to mid-July, and none of the three providers knew until Dragos told them. Its prompts were processed alongside real customer requests, and Moore says those “were almost certainly copied too”. In the largest breach, a couple of hundred AWS keys sent during a few short windows in late October were all stolen, some from requests the provider rejected before a model ran, which Dragos says means the attacker was copying traffic at the front door. In the other two, some stolen requests carried the Zero Data Retention (ZDR) flag, the strictest privacy setting.
The attackers tested keys, sometimes within hours, hunted for data and tried to switch on models in AWS Bedrock: tens of thousands of AWS API calls in all. One attacker appeared to be inside two providers at once and on November 1 added ARTEX, an AI-driven hacking tool. Dragos hasn’t named the providers. It says the first has still not disclosed its breach, while one of the late-October victims has published a preliminary security notice.
AI marketplace sellers read the prompts too
Many apps reach models through AI routers, which forward each request to models at other hosting companies. “Every hop can see the entire prompt and response,” Moore writes. On open marketplaces the cheapest seller gets the request, so a seller can undercut rivals, switch on logging and wait.
Dragos caught exactly that. About a day and a half after two prompts went through one seller, someone on a home broadband line opened both secret links and started guessing usernames; the same model bought from another seller was never touched. Elsewhere, a Mac on a home connection in France took passwords from two prompts and tried, by hand, to log in as root.
Tracing about 2,000 routes, Dragos found several hundred with a system it couldn’t identify. In one example, a marketplace seller’s request reached Anthropic through an OpenRouter hop the marketplace never disclosed. Routers like OpenRouter already face new rules from OpenAI on reselling its models.
“Zero Data Retention is supposed to mean something”
The third finding involved links scraped by companies that should never have seen the prompts. An unnamed Chinese AI lab fetched the secret links from more than half the prompts sent to its models between July and October, including about two-thirds of those marked “no data collection” or ZDR. Prompts sent to US hosts that resell its models set off the same scraper. One large US provider kept crawling a secret link more than two months after a single request.
Strangest of all, 24 days after a prompt sent with the ZDR flag, its secret link was posted in a chat on Feishu (Lark outside China) and opened within two minutes from six devices in Beijing and Shanghai. Moore sums it up:
Zero Data Retention is supposed to mean something. In practice, these prompts were retained, shared with other companies, and read by people.
HD Moore, chief research officer, Dragos
What you can do
Dragos is working with about a dozen providers and says stolen keys are still being used months later. Its advice: host models yourself for the most sensitive work, go straight to a major provider, pick a router’s upstream providers by hand, avoid reseller marketplaces (some cut-price capacity is billed to stolen keys, as AI account hijacking spreads), turn on secret filtering and plant your own fake credentials, such as a free Thinkst Canarytoken. AI coding agents add to the risk, since they can leak keys on their own:
Keep in mind that a privacy flag only binds the first hop, and that AI agents will happily send whatever they can read, including credentials.
HD Moore, chief research officer, Dragos
Why it matters
Businesses pour source code, plans and passwords into AI tools on the promise that privacy settings protect them. Dragos’s canaries show those settings often stop at the first company in a chain most customers never see, and that real attackers are already mining it.
Sources: Dragos, “Three breaches, endless leaks: Your AI supply chain needs canaries” (HD Moore).
Latest Policy & Safety news