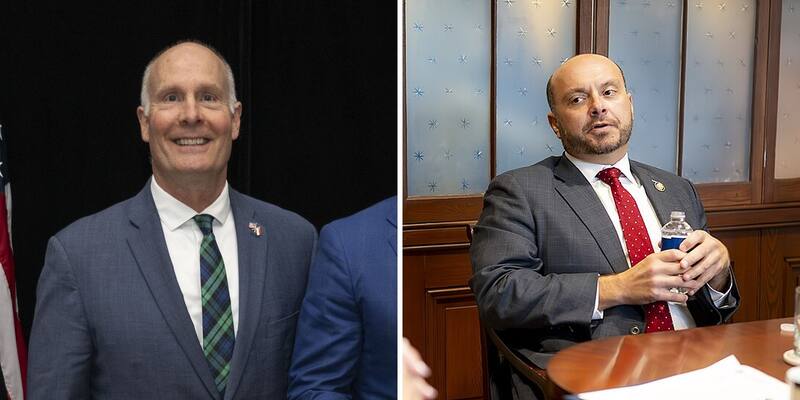
John Moolenaar, chair of the House Select Committee on China (left), at the Shangri-La Dialogue in Singapore in May 2025, and Andrew Garbarino, chair of the House Homeland Security Committee, at DHS headquarters in September 2025. File photos. Image: Moolenaar: US Navy Petty Officer 1st Class Alexander Kubitza, Department of Defense (public domain); Garbarino: Tia Dufour, Department of Homeland Security (public domain); both via Wikimedia Commons
China’s military went shopping in July for a cyber range that had to plug in DeepSeek to support “intelligent attack” and “intelligent penetration”, according to a joint report two House committees released on Friday. The same report says Chinese AI models are already running inside Airbnb, DoorDash and Cursor, and calls for banning them from federal systems.
What China’s military was buying
The report comes from the House Select Committee on China, chaired by John Moolenaar, and the House Homeland Security Committee, chaired by Andrew Garbarino, both Republicans. They reviewed procurement records from the People’s Liberation Army (PLA). The cyber range, a system for building “cybersecurity professional capability”, is in effect a training ground for military hackers. Other 2026 records describe:
- A command system: servers for an “intelligent command information system” built to run Alibaba’s Qwen and DeepSeek.
- An offline agent project: DeepSeek, Qwen, Moonshot’s Kimi and MiniMax models running on a network with no internet access, for military AI agent and software development.
The records show what the PLA set out to buy; the report doesn’t show any of these systems being used in a real attack. An annex says people linked to the 1st Bureau of the PLA Cyberspace Force, the unit the report says handles cyber espionage and attack, have visited the Beijing headquarters of Zhipu several times, most recently in August. The committees assess “with moderate confidence” that this points to a channel between them. Zhipu’s newest open-weight model is the one Anthropic said in September could build working cyber exploits on its own.
Airbnb, DoorDash and Cursor
The committees used three American companies as case studies:
- Airbnb runs customised Qwen models on US-based servers. One powers an AI assistant handling about 80,000 guest and host conversations a day; another summarises about 250,000 support cases and calls a day. Chief executive Brian Chesky has called Alibaba’s model “fast and cheap”.
- DoorDash told the committees its engineers had downloaded or tested models from at least six Chinese developers, and that 25 Chinese model families had been deployed “in a non-trivial manner”, meaning at least $5,000 in computing costs. Replacing one model built into a larger system could take up to six months, though most other uses could switch almost at once.
- Anysphere built Composer 2, the flagship model in its Cursor coding app, on Moonshot’s Kimi K2.5, which came out only after an independent developer spotted it. Anysphere told the committees it plans to explore phasing out Chinese open-weight models because of geopolitical risk.
Neither Airbnb nor DoorDash had paid a Chinese developer or signed a deal with one, and both run the models on US infrastructure, which the report says substantially reduces the risk of user data going straight to China. The committees’ worry is dependence: after the White House accused Moonshot of illicitly copying an American model, DoorDash said it had changed nothing about how it uses Kimi.
“Beijing is using stolen intelligence to close the gap”
The report says Chinese labs can sell cheap because state funds and subsidised computing cover their losses, and that their progress rests partly on outputs taken from American models, the tactic OpenAI accused Moonshot of in September. It warns that licence terms are tightening and that Beijing has weighed limits on overseas access. The chairmen write in the foreword:
While America is investing billions and racing to build ‘Super Intelligence,’ Beijing is using stolen intelligence to close the gap.
Andrew Garbarino and John Moolenaar, committee chairmen, in the report’s foreword
They also cite the South Korean bank breaches, where reports say the attacker used a Chinese hacking tool running on DeepSeek and Zhipu models.
12 recommendations
The main recommendations:
- Build an American alternative: a national open-weight AI initiative.
- Go beyond DeepSeek: extend the Homeland Security Department’s DeepSeek ban to all Chinese-developed models and their derivatives in federal systems and federal contract work, phase them out of high-risk critical infrastructure, and bar federal cyber grants from paying for them.
- Know what’s running: a model provenance standard and an “AI bill of materials”.
- One place to report: CISA as the single point for AI-related cyber incident reports, plus an independent board to investigate big ones.
- Punish copying: sanctions and Entity List listings for illicit distillers, and a review of sales of American training data to Chinese labs.
A classified annex went to cleared members. None of the recommendations is law yet.
Why it matters
Chinese open-weight models are now built into apps millions of Americans use, often with no contract or payment trail to show it. If Congress acts on this report, any company with federal contracts would have to find out exactly which models it runs, and replace the Chinese ones.
Sources: House Homeland Security Committee and Select Committee on China, joint investigative report on PRC open-weight AI models (PDF); House Homeland Security Committee press release; Select Committee on China press release.
Latest Policy & Safety news